OPEN FOR EARLY ACCESS

Less guesswork.More proof.

The next change deserves more than a green check.

Review API releases before wider rollout. Verify AI-written code independently. Keep the evidence behind every decision.

TWO PRODUCTS. ONE PRINCIPLE: EVIDENCE BEFORE RELEASE.
RELAYOPS / RELEASE CONTROLILLUSTRATIVE DEMO
Release workspacerev / demo
APIorders / candidateIN REVIEW

A change.
A clear next step.

01
Review the changeConfiguration + consumer impact
✓
02
Test the candidateRequired checks on the deployed revision
✓
03
Own the decisionAdministrator review + release evidence
✓
Review the plan before canary exposure.↗
Evidence travels with the change.Reviewed inputs → recorded outcome
BUILT FOR THE WAY YOU SHIP
API & platform teams+AI-assisted engineering+Your existing CI
01 / CHOOSE YOUR WORKFLOW

Different changes.
The same need for proof.

Start with the problem your team is solving today.

01APACHE 2.0 · EARLY ACCESS

API Management

From API contract
to a reviewed release.

A gateway, release workspace and developer portal. Review consumer impact, deploy a canary and check the evidence before promotion.

  • Canary releases + automatic rollback
  • Required candidate checks + explicit review
  • Self-service consumer onboarding
02DESIGN-PARTNER PILOT

Code Assurance

The author writes it.
Independent checks verify it.

Re-run AI-written changes in a clean environment. Surface weakened tests and issue a signed Change Passport tied to the exact code.

  • GitHub Actions + GitLab CI
  • Explicit VERIFIED, FAILED or INCOMPLETE outcomes
  • Open in-toto + DSSE evidence formats
02 / INSIDE RELAYOPS

See the work.
Inspect the evidence.

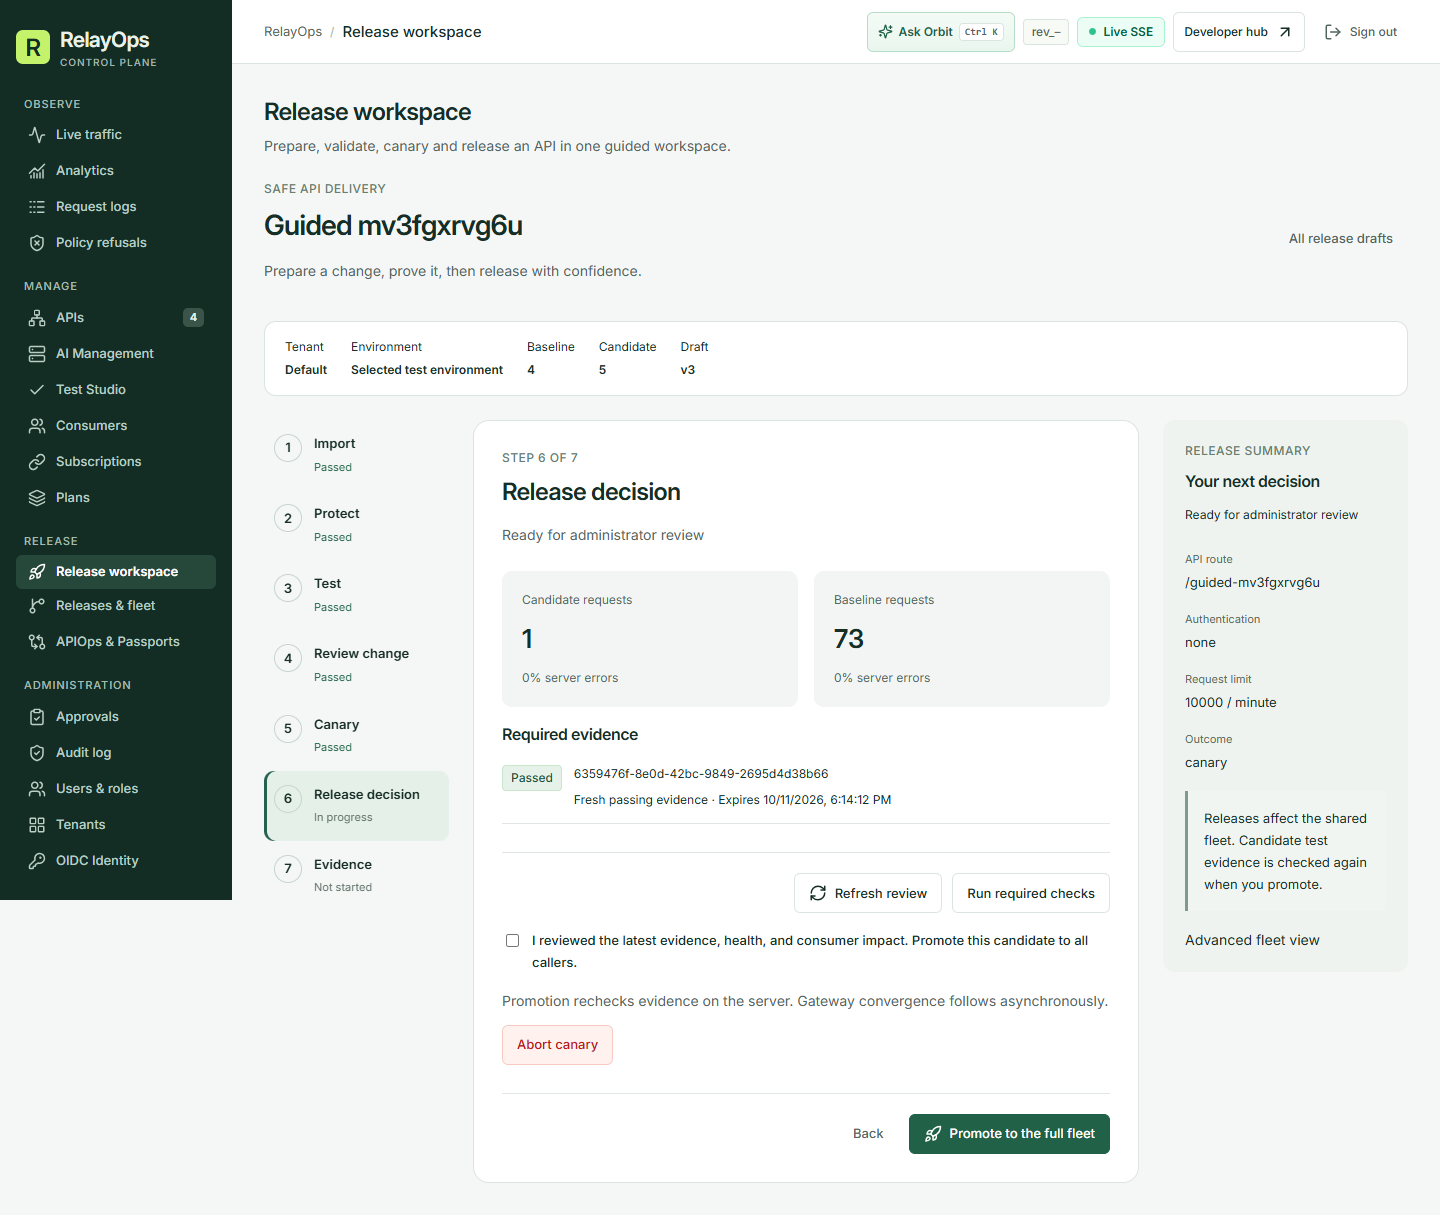
Real product screens. Explore the release workspace or follow a change to its signed verification receipt.

RelayOps / Release workspace
RelayOps release workspace showing required evidence and administrator review
REVIEWED RELEASES

The next step is visible.

Review the candidate, required checks and administrator decision together. This product screen uses sample traffic and test settings, not customer production data.

Walk the release journey ↗
03 / EVIDENCE BEFORE AUTONOMY

A green check
is only the beginning.

Code Assurance records what was verified, what was missing and exactly which code was checked.

01 / RE-RUN

Check independently.

Run the base and head commits in a clean environment. Inspect test integrity, dependencies and secrets alongside the test result.

02 / RECORD

Make missing proof visible.

A test that needs an unavailable secret is incomplete. It should never become an invented success or a failure blamed on the change.

03 / BIND

Keep proof tied to the code.

Sign the result over the commits and verification inputs. A new commit or moved base makes the previous proof stale.

CHANGE PASSPORTILLUSTRATIVE
orders / update-validation
Checking independently
Base + head commitsBOUND
Verification inputsRECORDED
Unavailable checksEXPLICIT
$ relayops verify

Re-run the change.
Compare it with the base.

An explanation of the workflow, not a live verification run.
04 / SHOW YOUR WORK

Small sample.
Open evidence.

Our published study covers 15 real open-source pull requests. Read the method, individual outcomes and limitations before drawing conclusions.

Read the PR studies ↗
11

VERIFIED

Changes with test suites that could run in the sandbox.

↗
04

INCOMPLETE

Tests needed secrets or network access that was unavailable.

—

Reported study results, not an independent audit, customer outcome or production guarantee.

05 / EARNED AUTONOMY

Observe first.
Gate when you're ready.

Start alongside your existing CI. Make release policy a deliberate decision.

L0 / OBSERVE

Measure before you govern.

Attach informational Change Passports to pull requests. See what verification finds without blocking merges.

mode: observe
action: verify + record_passport
merge_gate: false
Plan a pilot with us ↗
06 / TRUST, IN THE DETAILS

Clear boundaries.
Inspectable proof.

↳

Runs where your code is.

The verification step runs in your GitHub Actions or GitLab CI, with a deny-by-default sandbox network.

⌁

Open formats. Offline checks.

Verify a Passport signature locally with the public key. No call back to RelayOps is required.

Try the verifier ↗
◎

Today and planned.

Development signing keys today. Production KMS signing and SOC 2 Type I are planned. Evidence is not certification.

Read the security details ↗
BEFORE YOU START

A few good
questions.

For platform teams, engineering leaders and security reviewers evaluating a bounded pilot.

Which product should I start with?+

Choose API Management if you need a gateway, reviewed API delivery and consumer onboarding. Choose Code Assurance to independently verify AI-written pull requests and inspect signed Change Passports. You can evaluate either product on its own.

Does RelayOps replace our CI?+

No. Code Assurance runs alongside GitHub Actions or GitLab CI. API Management provides its own release workspace and required candidate checks.

Can we self-host API Management?+

Yes. The API Management repository is open source under Apache 2.0. Start with the quickstart, or discuss a hosted pilot in Sydney.

What does early access mean?+

Start with a bounded workload and agreed operating requirements. Independent security assessment, measured recovery commitments and broader production validation remain milestones. We do not claim enterprise SLAs or certified compliance.

Model the opportunity with your own numbers ↗
ILLUSTRATIVE REVIEW CAPACITY

Your assumptions.
Your estimate.

No measured savings are claimed. This estimates annual review capacity only, using 220 working days and a $110/hour loaded rate.

Illustrative annual capacity$45,375

LET'S START WITH ONE CHANGE

Bring your workflow.
We'll bring the questions.

Evaluate one API or one repository. Agree on the boundaries, inspect the evidence and decide what comes next.

RelayOps / Product screen
RelayOps release workspace enlarged