Protect your APIs
Configure authentication, subscription approvals, rate limits and quotas. Keep secret references in release drafts rather than inline credentials.
A gateway, release workspace and developer portal. One clear path from an OpenAPI contract to a reviewed release—and from discovery to the first authorized request.
For HTTP/OpenAPI releases. Open for early-access teams: hosted on AWS in Sydney, or self-hosted from the open-source image.
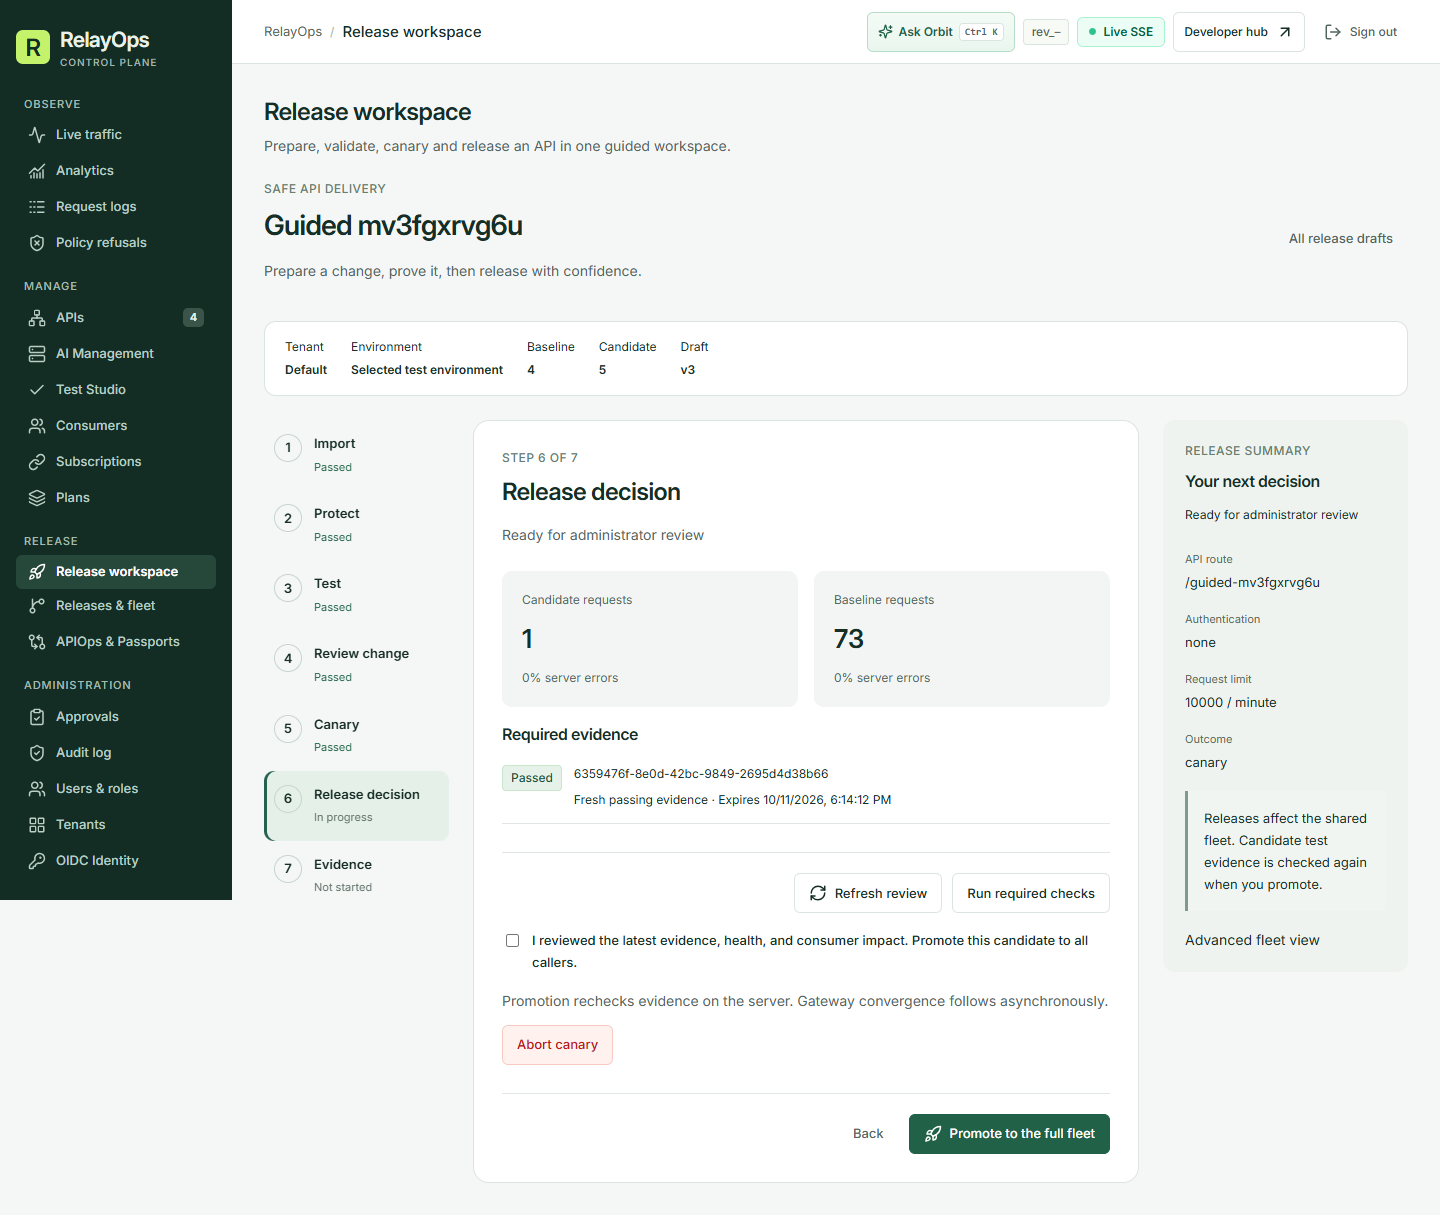
Prepare changes separately from live configuration. Deploy a candidate, run its required checks, then review the evidence before promoting or aborting.
Candidate checks run after deployment. Missing, failed, skipped, expired or changed-input evidence blocks promotion. The server checks eligibility again when the administrator confirms.
Consumers keep their selected API and application throughout onboarding. Approval requirements appear before registration, and pending access never appears ready.
The operator screen brings the release steps, candidate and baseline context, required evidence and final administrator review into one workspace.
Configure authentication, subscription approvals, rate limits and quotas. Keep secret references in release drafts rather than inline credentials.
Use versioned drafts, reviewed plans, required tests and canary exposure. Export evidence tied to the actual promotion decision.
Published documentation, plan requirements and application access lead into an explicit first request, then usage monitoring.
Evaluate the product against your workload and operating requirements. Production commitments require measured results and accountable ownership.
No certified uptime, recovery objective, independent assessment or customer outcome is claimed here. Kubernetes production parity follows the AWS VM validation target.
Start with a bounded, noncritical workload. Review your deployment, access policy, release checks and recovery requirements with the RelayOps team.